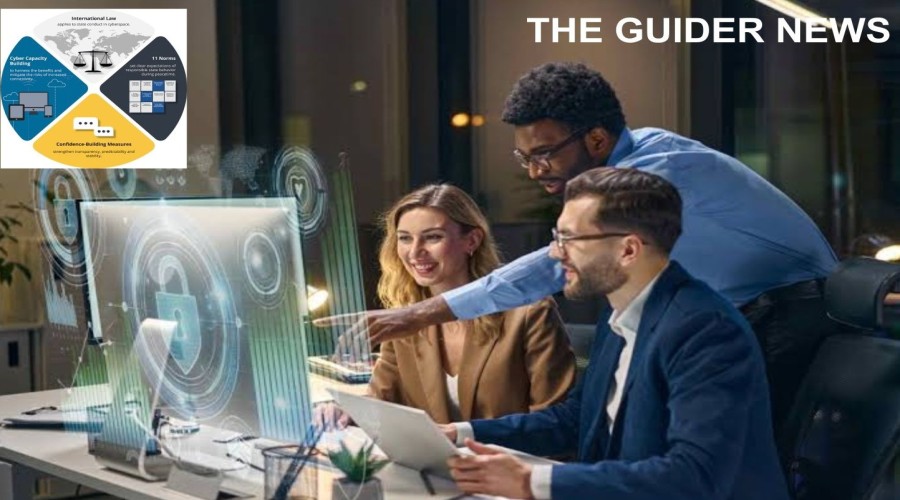
ISLAMABAD: The protection of critical infrastructure is becoming an increasingly important cybersecurity priority as governments and businesses rely on interconnected digital and operational systems to deliver essential services.
Modern infrastructure depends on technology across sectors including energy, finance, healthcare, transport, telecommunications and public services. As these systems become more connected, the consequences of a successful cyber incident can extend beyond a single organisation.
Singapore has been strengthening its approach to protecting Critical Information Infrastructure (CII) while responding to changes in the global cyber threat environment. The Cyber Security Agency of Singapore said in June 2026 that its Singapore Cyber Landscape 2025/2026 report identified growing complexity, speed, scale and sophistication in cyber threats.
The report highlighted artificial intelligence and supply-chain interdependencies among the factors influencing the changing environment. It also reported an increase in ransomware attacks in Singapore and pointed to a broader attack surface associated with Malware-as-a-Service operations and vulnerable Internet-of-Things devices.
The growing dependence on suppliers and interconnected services creates a particular challenge for critical infrastructure operators. An organization may maintain strong internal security controls but still face risks through software providers, cloud services, managed service providers or other connected partners.
Supply-chain security therefore requires organisations to understand not only their own systems but also the technologies and services on which they depend. This can involve security requirements for suppliers, monitoring, vulnerability management, incident reporting and contingency planning.
Artificial intelligence is adding another layer to this challenge. CSA has warned that AI-enabled threats can allow attackers to operate more quickly and at greater scale. In July 2026, the agency announced an updated Cybersecurity Code of Practice for Critical Information Infrastructure and said the update responds to changes in the threat landscape, including advanced persistent threats and AI-enabled threats.
The updated framework reflects the need for cybersecurity practices to evolve as technology changes. Critical infrastructure operators cannot rely exclusively on security measures designed for an earlier generation of digital systems when networks, cloud services, connected devices and AI capabilities are changing rapidly.
Singapore has also been working to improve preparedness through exercises and broader cybersecurity programmes. CSA said its 2025 Exercise Cyber Star involved close to 500 participants from the agency, the Singapore Armed Forces’ Digital and Intelligence Service and critical infrastructure owners across 11 sectors. The exercise tested responses to large-scale cyber incidents affecting national critical infrastructure.
Exercises are important because technical controls alone cannot guarantee an effective response to a major cyber incident. Organisations also need clear procedures for communication, decision-making, containment, recovery and coordination with government agencies and other affected parties.
The international dimension is equally important. Cyber incidents do not respect national borders, and attacks on globally connected infrastructure can involve actors, victims, service providers and data located in different jurisdictions. Cooperation between governments and the private sector is therefore an important part of cyber resilience.
These issues will be part of the broader discussion at Singapore International Cyber Week 2026, scheduled for 12 to 15 October. SICW 2026 is being held under the theme “Cyber at a Crossroads: Shaping the New Cyber Order,” reflecting concerns about AI-enabled threats, attribution challenges, evolving state behaviour in cyberspace and fragmentation of the digital ecosystem.
The event brings together policymakers, diplomats, technical experts, industry leaders and academics. Such a mix is significant because critical infrastructure security requires decisions at several levels. Technical teams are responsible for protecting systems, executives make investment and risk decisions, governments establish regulatory frameworks, and international partners may be needed when incidents cross borders.
Cloud computing is also becoming an important part of this discussion. CSA announced in July that a new Cybersecurity Code of Practice for Cloud Services would be launched later in 2026. The move reflects the growing role of cloud infrastructure in the digital economy and the need to address security responsibilities in increasingly shared environments.
For critical infrastructure operators, resilience increasingly means preparing for disruption rather than assuming that every attack can be prevented. Detection, incident response, backup systems, recovery planning and coordination can determine how quickly essential services are restored.
The cybersecurity challenge facing critical infrastructure is therefore broader than preventing unauthorised access. It includes maintaining continuity, protecting supply chains, securing emerging technologies and ensuring that organisations can coordinate during major incidents.
As SICW 2026 brings together stakeholders from different parts of the global cybersecurity community, critical infrastructure is likely to remain central to discussions about trust, resilience and international cooperation. The underlying challenge is to ensure that digital transformation continues while security measures evolve at the same pace.
 Reported By : Mirza Maqbool Baig I Islamabad